Trust Services Criteria
Every SOC 2 report covers Security. Add the other criteria your customers need.
Security is required in every report. The other four criteria are optional, based on what your customers expect.
Security
Systems and data are protected against unauthorized access. Required in every SOC 2 report.
Availability
Systems are available for operation and use as committed.
Processing Integrity
Processing is complete, valid, accurate, timely, and authorized.
Confidentiality
Information designated as confidential is protected.
Privacy
Personal information is collected, used, kept, and disposed of properly.
The Basics
What Is a SOC 2 Audit?
A SOC 2 audit gives your customers, investors, and others assurance that your organization's controls protect the information in your environment and fit the purpose they're meant for.
Each SOC 2 report includes an in-depth review of at least one of the AICPA Trust Services Criteria: security, availability, processing integrity, confidentiality, and privacy.
Performed under
- AICPA SSAE No. 18
- AT-C 105 and AT-C 205
- Trust Services Criteria (TSP Section 100): the criteria we use to evaluate the design and operating effectiveness of your controls across Security, Availability, Processing Integrity, Confidentiality, and Privacy
- Description Criteria (DC Section 200): the criteria management uses to prepare, and we use to evaluate, the description of your system
- AICPA SOC 2 Guide: Reporting on an Examination of Controls at a Service Organization Relevant to Security, Availability, Processing Integrity, Confidentiality, or Privacy
Report Types
Type I or Type II?
Our team performs both, and we'll help you decide which report you need.
| Compare | Type I | Type II |
|---|---|---|
| What it covers | A description of your system and a test of the design of your controls. | Everything in a Type I, plus the operating effectiveness of key controls. |
| Time covered | As of a specific date. | A period of time, typically 6 to 12 months. |
| Shows customers | Controls are designed and in place. | Controls worked throughout the period. |
How a SOC 2 Audit Works
A Clear, Collaborative Process.
From scoping to report delivery, with regular communication throughout. See our full process.
Scoping call
We learn how your services work and which Trust Services Criteria your report needs.
Fee & timeline
You get a specific written fee and a timeline, so you know what to expect and when.
Readiness assessment (optional)
For a first SOC 2, a dry run of the examination that ends in a management letter listing any gaps to address before the audit period.
Request list & controls matrix
We send a to-do list and a risk and controls matrix to speed up the audit.
Testing
Onsite or virtual interviews and testing, with as little disruption to your team as possible.
Report delivered
Your SOC 2 report is delivered digitally, along with a formal management communication.
What Drives the Cost
What Does a SOC 2 Audit Cost?
The fee depends on your scope. These are the main factors.
Type I or Type II
A Type II report tests controls over a period of time, so it takes more testing.
Criteria in scope
Adding Availability, Confidentiality, Processing Integrity, or Privacy to Security adds work.
Systems & locations
The size and complexity of your systems, and any locations we need to visit.
Subservice organizations
How many outside providers, such as cloud hosts, your services rely on.
Control maturity
Well-documented controls, and whether this is a first-year audit or a renewal.
Combined frameworks
Adding HIPAA, ISO 27001, or another framework to the same engagement.
You get a specific, written quote before work begins.
Why Linford
A Higher Standard for SOC 2 Audits.
SOC Reports Every Day
SOC examinations are a core part of our practice. We know how to get you from kickoff to report quickly and accurately.
Partner Involvement
A partner is involved in most examinations from start to finish, because quality and efficiency start at the top.
Responsive Team
SOC 2 is demanding. You get an experienced, responsive team that knows both the technology and the standards.
Our Partners
Experienced, Credentialed IT Auditors.
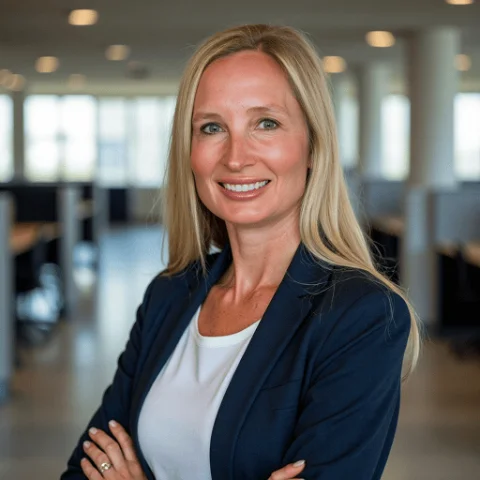
- Nicole Hemmer
Partner
CISSP, CISA
Co-founder of Linford & Company LLP who specializes in SOC examinations, after beginning her career at Ernst & Young.
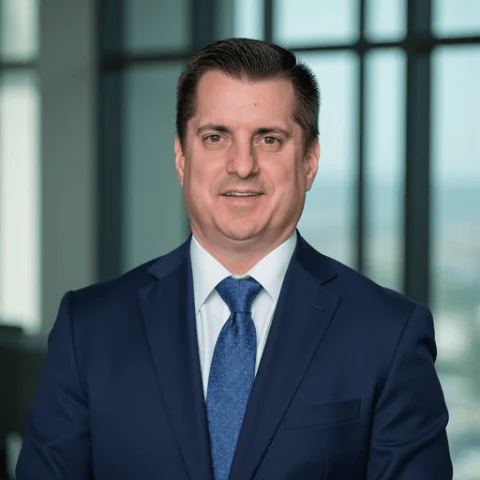
- Isaac Clarke
Partner
CPA, CISA, CISSP, CCSFP, ISO 27001 Lead Auditor
Specializes in SOC, HIPAA, HITRUST, and ISO assessments for companies from startups to the Fortune 100. Began his career at Ernst & Young.
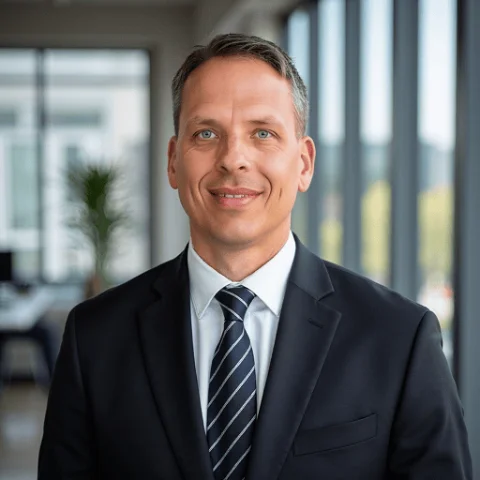
- Mark Larson
Partner
CISSP, CISA, QSA, CMMC Lead Certified Assessor (Lead CCA), CCP, ISO 27001 Lead Auditor
Specializes in SOC examinations, after six years at Ernst & Young and leadership roles in internal audit, technology, and security.
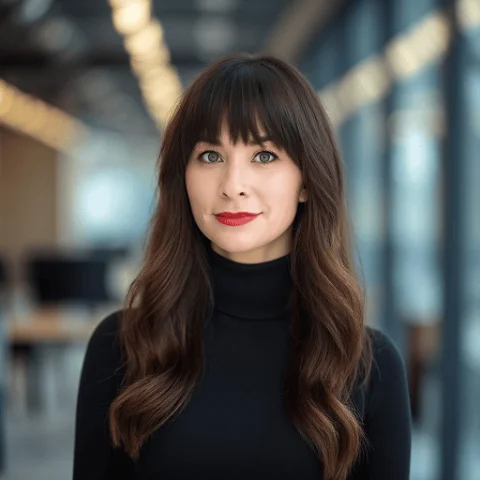
- Megan Kovash
Partner
CPA
Nearly 14 years in IT audit and assurance, specializing in SOC audits. Began her career at Ernst & Young.
Get started
Talk With a SOC 2 Partner.
Tell us about your services, your customers' requirements, and your timing. A partner will follow up to learn more, and you get a specific, written quote before any work begins.
- Type I or Type II, with the criteria your customers expect
- A partner involved in most examinations from start to finish
- No fees quoted until we understand your scope
SOC 2 Questions
Frequently Asked Questions.
How does a SOC 2 audit begin?
We meet with your management team to understand your services and your customers' needs. From that, we determine which Trust Services Criteria belong in your SOC 2 examination.
Who will we work with?
A partner scopes your audit, sets the fee, and leads the engagement, working with a small, experienced team. On most engagements, the same partner is involved from the scoping call to the final report. We don't have salespeople, and we have no offshore staff.
Do you offer readiness assessments?
Yes, for SOC 1 and SOC 2. A readiness assessment is a dry run of the examination before your first audit. Instead of a SOC report, you receive a management letter that lists any gaps we identify, so your team can address them before the audit period or report date. Your team remains responsible for designing and fixing its controls.
When will we see the fee and timeline?
Once we understand your system and the criteria in scope, we give you a specific fee and a timeline before work begins. That greatly reduces the risk of fee increases later.
Will the audit disrupt our team?
We work to keep disruption to a minimum while still gathering what a complete and accurate SOC 2 examination needs. Interviews and testing can be onsite, virtual, or both.
What do we receive at the end?
A professional SOC 2 report, delivered digitally so you can share it easily with customers and others. If we see ways to improve your processes or controls, we include recommendations.
From the blog
Learn more from our auditors
- What Is SOC 2 Compliance? Requirements, Reports and Audits ExplainedRead the article →
- Trust Services Criteria (TSCs) for SOC 2 ReportsRead the article →
- SOC Report Types: Type 1 vs Type 2 SOC ReportsRead the article →
- The SOC 2 Risk Assessment Criteria: Through the Eyes of an AuditorRead the article →
Let's get started
Talk to a partner, not a sales team.
Get a specific, written quote for your SOC 2 audit before any work begins.