Home / About / Leadership Team

Leadership Team

The Auditors Behind Every Report.

Our partners stay closely involved in the work. Most trained at the world's largest firms, and all of them focus on IT audit.

20Partners
Big FourOur partners include alumni of EY · PwC · KPMG · Deloitte
100%Partner-owned, independent

Our partners

Meet the partners

Filter by audit type, then open a profile to read a partner's background or send them a message.

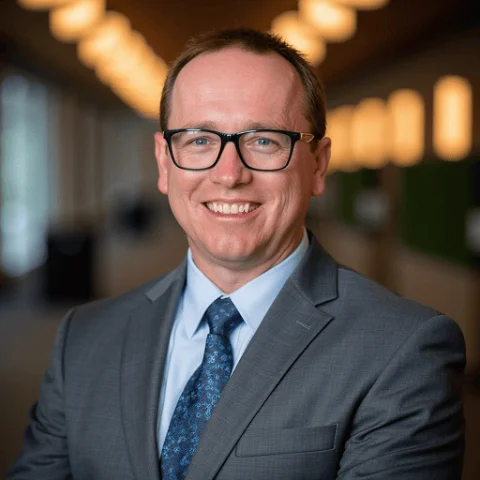
Newel Linford

Newel Linford

Managing Partner

  • CPA
  • CISA

SOC 1 & SOC 2 examinations

View bio

Newel has over 20 years of internal control and audit, IT assurance and advisory, and accounting experience; 9 of those years were with a “Big Four” accounting firm. During his career, he has been responsible for a significant number of SOC 1 audits and SOC 2 audits for companies spanning a variety of industries. Newel has developed SOC training content, led SOC training, and acted as the SOC quality leader for an entire “Big Four” region within the United States. He has also guest lectured at several universities on various topics related to advancements in information technology accounting. He is a certified public accountant (CPA) in the state of Colorado, a certified information systems auditor (CISA), and a member of the American Institute of Certified Public Accountants (AICPA), ISACA and the Colorado Society of CPAs. Newel holds a Bachelor of Science in Accounting and Information Systems degree from Brigham Young University.
Full profile and contact
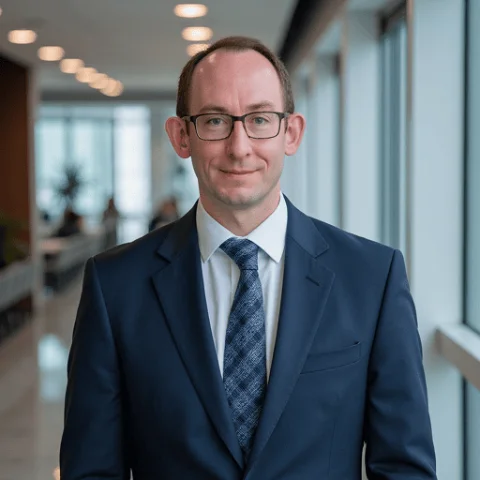
Nicole Hemmer

Nicole Hemmer

Partner

  • CISSP
  • CISA

Co-founder · SOC and GDPR examinations

View bio

Nicole Hemmer started her career in 2000. She is the co-founder of Linford & Company LLP. Prior to Linford & Company LLP, Nicole worked for Ernst & Young in Indianapolis, Chicago, and Denver. She specializes in SOC examinations and loves the challenge that comes with clients across all industries. Nicole loves working with her clients to help them through examinations for the first time and then working together closely after that to have successful audits.

Full profile and contact
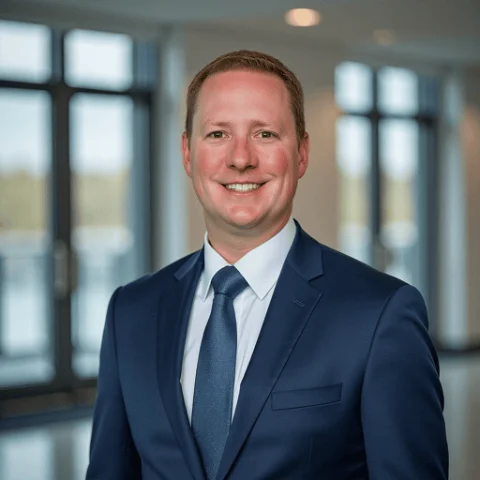
Rob Pierce

Rob Pierce

Partner

  • CISSP
  • CISA
  • CCSFP
  • CHQP

Helps lead the HITRUST practice

View bio

Rob started with Linford & Company LLP in 2011 and helps lead the HITRUST practice as well as performs SOC audits, NIST 800-171, and HIPAA assessments. He has spoken at Data Center World on compliance-related topics and has completed over 800 SOC examinations. He started his career as an IT auditor in 2003 with PwC in the Systems and Process Assurance group, and has worked in a variety of industries in internal audit as well as for the City and County of Denver.

Full profile and contact
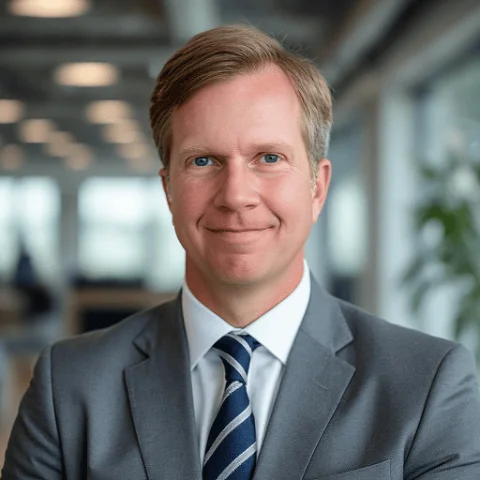
Ray Dunham

Ray Dunham

Partner

  • CISSP
  • CISA
  • GSEC
  • GWAPT

FedRAMP & SOC

View bio

Ray Dunham started his career as an Air Force Officer in 1996 in the field of Communications and Computer Systems. Following his time in the Air Force, Ray worked in the defense industry in areas of system architecture, system engineering, and primarily information security. Ray performs FedRAMP assessments and also supports SOC examinations. He brings a practitioner’s understanding of information security to every assessment and works closely with clients to keep each engagement well organized and efficient.

Full profile and contact
Isaac Clarke

Isaac Clarke

Partner

  • CPA
  • CISA
  • CISSP
  • CCSFP
  • ISO 27001 Lead Auditor

SOC · HIPAA · HITRUST · ISO 27001

View bio

Isaac Clarke is a partner at Linford & Company LLP. He began his career with Ernst & Young in 2003 where he developed his audit expertise over a number of years. Isaac specializes in and has conducted numerous SOC, HIPAA, HITRUST, and ISO assessments for a variety of companies, from startups to Fortune 100 companies. Isaac enjoys helping his clients understand and simplify their compliance activities. He is attentive to his clients’ needs and works meticulously to ensure that each examination and report meets professional standards.

Full profile and contact
Jaclyn Finney

Jaclyn Finney

Partner

  • CISA
  • ISO 27001 Lead Auditor

SOC · FedRAMP · ISO

View bio

Jaclyn Finney has spent 17 years in audit, starting in 2009 and joining Linford & Company LLP in 2016. As a partner, she has helped hundreds of clients through SOC 2 and ISO 27001 audits, and she also works on SOC 1 examinations and ISO 27701 privacy certifications as an ISO partner. She is a CISA and an ISO 27001 Lead Auditor, and she supports the firm's FedRAMP practice as a partner. Her clients range from SaaS companies to data centers, healthcare organizations, and government contractors. Jaclyn tailors each engagement to the client's environment and delivers a report that is useful to the client and to the people who rely on it.

Full profile and contact
Megan Kovash

Megan Kovash

Partner

  • CPA

SOC & IT security audits

View bio

Megan Kovash has nearly 14 years of experience in IT audit and assurance, specializing in SOC audits, with experience in financial audit, internal audit, and data analytics. Megan started her career in 2012 at Ernst & Young prior to joining Linford & Company LLP in 2019. Megan is a partner with the firm, a certified public accountant (CPA) in the state of Colorado, and a member of the American Institute of Certified Public Accountants (AICPA). Additionally, she holds a Master of Accountancy from the University of Denver. Megan works closely with clients to plan efficient audits that meet their reporting requirements, with clear communication from planning through the final report.

Full profile and contact
Maggie Cheney

Maggie Cheney

Partner

  • CRISC
  • ISO 27001 Lead Auditor

Risk & IT compliance

View bio

Maggie has 20 years of experience in Risk Management and IT Compliance. She spent nearly 10 years in KPMG’s IT Advisory and Attestation practice before joining a financial technology company as the Risk and Compliance Director, where she was responsible for implementing the company's Risk and Compliance framework. She has overseen numerous SOC 1 / SOC 2 audits and other IT compliance audits (HIPAA, ISO) and has vast experience implementing risk management and IT compliance solutions. She is Certified in Risk and Information Systems Control (CRISC) and obtained a Bachelor of Science in Business Administration, Finance, from the University of Colorado at Boulder.

Full profile and contact
Mark Larson

Mark Larson

Partner

  • CISSP
  • CISA
  • QSA
  • CMMC Lead Certified Assessor (Lead CCA)
  • CCP
  • ISO 27001 Lead Auditor

SOC examinations

View bio

Mark Larson started working in the technology industry in 1998 where he worked in a number of different roles prior to transitioning to the public accounting world in 2004 with Ernst & Young (EY). During his 6 years at EY, Mark provided both assurance and advisory services that spanned multiple industries for both public and private companies. After leaving EY, Mark filled leadership roles within Internal Audit, Technology, and Security functions for several companies. Mark specializes in SOC examinations and enjoys helping clients establish, formalize, and report on effective control environments while strengthening their security risk profile.

Full profile and contact
Lois Colby

Lois Colby

Partner

  • CPA
  • CIA
  • CISA
  • CCSK
  • CMMC Lead Certified Assessor (Lead CCA)
  • ISO 42001 Lead Auditor
  • ISO 27001 Lead Auditor

SOC · HIPAA · ISO · CMMC · CSA STAR

View bio

Lois started with Linford & Company LLP in 2020. She began her career in 1989 and has spent her career working in public accounting at Ernst & Young and in industry focusing on SOC 1, SOC 2, other audit activities, ethics & compliance, governance, and privacy. At Linford, Lois specializes in SOC 1, SOC 2, HIPAA, ISO, CMMC, and CSA STAR audits. Lois’ goal is to collaboratively serve her clients to provide a valuable and accurate product that meets the needs of her clients and their customers all while adhering to professional standards.

Full profile and contact
Rhonda Willert

Rhonda Willert

Partner

  • CPA
  • CISSP
  • CISA
  • PMP
  • QSA
  • ISO 27001 Lead Auditor

SOC · HIPAA · ISO · HITRUST

View bio

Rhonda is a Partner at Linford & Company LLP delivering risk services, compliance attestations, and certification engagements. Rhonda has her CPA, CISSP, CISA, ISO Lead Auditor Certification, and her PMP certification. Previously, Rhonda was a Managing Director at Deloitte, and brings a wealth of expertise in the areas of risk management and compliance and delivers excellent client service. Rhonda actively supports clients in all industries and focuses on compliance frameworks such as SOC 1, SOC 2, HIPAA, HITECH, ISO/IEC 27001:2022, ISO/IEC 27017, ISO/IEC 27018, NIST 800-171, and HITRUST.

Full profile and contact
Kevin Anderson

Kevin Anderson

Partner

  • CPA
  • ISO 27001 Lead Auditor

SOC audits, ISO 27001 & IT assurance

View bio

Kevin has over ten years of experience in internal controls, audit, and advisory work. Kevin started his career in public accounting at Deloitte focusing on internal controls, SOC audits, and IT assurance work. After Deloitte, Kevin filled a leadership role in the SOX Compliance group at a financial services company. Kevin is a CPA, an ISO 27001 Lead Auditor, and holds a Bachelor of Science degree in Accounting from Brigham Young University and a Master of Business Administration degree from Ohio University.

Full profile and contact
Becky McCarty

Becky McCarty

Partner

  • CPA
  • CISA
  • CRISC
  • CIA
  • CFE
  • ISO 27001 Lead Auditor

SOC · HIPAA · ISO 27001

View bio

Becky McCarty has extensive experience in internal controls, audit, and advisory services. She specializes in SOC, HIPAA, and ISO/IEC 27001:2022 examinations for Linford & Company LLP. Becky completed a Bachelor’s degree in Business Administration (Accounting) and a Master of Science degree in Management Information Systems. She worked 6 years with KPMG LLP commencing in 1999, worked many years in the energy industry, and joined Linford & Company LLP in 2018. Becky also served 9 years on the Board of Directors for a home healthcare nonprofit. She works closely with clients so that the examinations are performed efficiently and with minimal disruption while ensuring performance in accordance with professional guidance. She enjoys helping clients successfully achieve the requirements for their security compliance reporting needs.

Full profile and contact
Hilary Stavrakas

Hilary Stavrakas

Partner

  • CISA

SOC · HIPAA · NIST

View bio

Hilary’s career in IT audit and assurance spans more than a decade, giving her the opportunity to work with start-ups who are newer to compliance and large corporations with well-established audit programs. During her time at Linford, and previously at Deloitte, she has developed extensive experience with SOC reporting, HIPAA compliance, NIST audits, and Sarbanes-Oxley (SOX) 404 examinations. Hilary is a Certified Information Systems Auditor (CISA), an ISO 27001 Lead Auditor, and holds a Master’s Degree in Accounting from the University of Colorado Denver and a Bachelor’s Degree in Business Administration from Colorado State University.

Full profile and contact
Jenny Shen

Jenny Shen

Partner

  • CISA
  • CISSP
  • CCSFP
  • QSA
  • ISO 27001 Senior Lead Auditor
  • ISO 27701 Lead Auditor

SOC · HITRUST · ISO · PCI

View bio

Jenny has been in risk advisory and compliance since 2008. She spent 7 years at Ernst & Young where she was responsible for both audit and advisory engagements across financial services, energy, technology, and healthcare sectors. Since 2015, she has been focusing on serving SaaS-based companies, assessing their control environments as part of SOC reporting, HIPAA compliance, ISO 27001 and HITRUST certification, and PCI compliance initiatives. She is a certified information systems auditor (CISA), HITRUST assessor (CCSFP), information systems security professional (CISSP), PCI QSA, ISO 27001 Lead Auditor, and AWS cloud practitioner. Jenny received her Bachelor of Science and Master’s degrees in Information Systems Management from Brigham Young University.
Full profile and contact
Danielle Pei

Danielle Pei

Partner

  • CISA

SOC · HIPAA

View bio

Danielle started her information systems compliance career in 2003 at PricewaterhouseCoopers in their Systems and Process Assurance group, followed by the Internal Audit Department of a financial services company and the IT compliance group for a large healthcare organization. She has experience in IT general control reviews, SOC audits, HIPAA compliance, Sarbanes-Oxley section 404 attestation engagements, and Payment Card Industry Data Security Standards (PCI DSS) compliance. Danielle is a Certified Information Systems Auditor (CISA) and received her Bachelor of Science degree in Management Science & Information Systems from Penn State University.

Full profile and contact
Richard Rieben

Richard Rieben

Partner

  • CISSP
  • CCSFP
  • CHQP
  • GSNA
  • QSA
  • CySA+
  • SecurityX
  • CMMC Lead Certified Assessor (Lead CCA)
  • CCP

HITRUST practice lead

View bio

Richard Rieben is a Partner and HITRUST practice lead at Linford & Company LLP, where he leads audits and assessments across HITRUST, SOC, CMMC, PCI DSS and NIST. With over 20 years of experience in IT and cybersecurity and certifications including PMP, CISSP, CCSFP, GSNA and SecurityX, Richard helps growing organizations meet their information security and compliance goals. He holds a Bachelor of Science in Business Management and an MBA from Western Governors University.

Full profile and contact
Ben Burkett

Ben Burkett

Partner

  • CPA
  • CISA
  • CISSP
  • CRISC
  • ISO 27001 Senior Lead Auditor
  • ISO 42001 Lead Auditor

SOC · HIPAA · ISO

View bio

Ben Burkett is a partner at Linford & Company, where he specializes in IT compliance and risk management audits. With more than twenty years of technology and audit experience that began at KPMG in 2002, Ben has led IT risk management initiatives, directed an IT Project Management Office and a Technology Business Management function, and served in finance and technology leadership roles. He holds certifications as a CPA, CISA, CISSP, CRISC, and as a Lead Auditor for ISO/IEC 27001 and ISO/IEC 42001. At Linford & Company LLP, Ben performs HIPAA, SOC 2, SOC 1 and ISO/IEC 27001 attestation and certification engagements, with a focus on efficient, risk‑based audits that deliver actionable insights.

Full profile and contact
Tim Nackos

Tim Nackos

Partner

  • CPA
  • CISA
  • ISO 27001 Senior Lead Auditor

IT assurance & data analytics

View bio

Tim Nackos joined Linford & Company LLP in 2022. The first 5 years of his career were spent at the “Big Four” firms EY and KPMG providing IT assurance and advisory services. He also spent 10 years at two large financial institutions primarily in internal audit performing data analytics. Tim is a certified public accountant (CPA) in the states of Utah and Arizona and is a certified information systems auditor (CISA). He holds both a Master of Accountancy and a Bachelor of Science degree in Accounting from Brigham Young University.
Full profile and contact
John Pohlmann

John Pohlmann

Partner

  • CISA

IT security, GRC & privacy

View bio

John has more than 20 years of experience focused on IT security, governance, risk, compliance, and privacy. He started his career in 2006 with Protiviti and later went on to run IT audit and GRC functions for several Fortune 500 companies within the financial services, energy, hospitality, and software industries. At Linford, John leads SOC 2 engagements for organizations of every size, from two-person startups to global software companies. John is also a Certified Information Systems Auditor (CISA) and holds a Bachelor of Science degree in Business Administration from Colorado State University.

Full profile and contact

Let's get started

Talk to a partner, not a sales team.

Tell us about your audit and a partner will reply personally.

Request a Consultation