Articles
-
PCI DSS
The New Era of PCI DSS 4.0: Requirements Effective After March 31, 2025
Learn PCI DSS 4.0's 47 mandatory requirements that are now in effect. Complete guide covering authentication, encryption, logging, and vulnerability management.
By Jenny ShenJuly 30, 2025 -
Compliance
Navigating Regulatory Compliance - An Auditor's Insights
Navigating regulatory compliance like HIPAA, GDPR, GLBA, and FISMA can be hard. Linford & Co. can help, with 16 years of expertise as certified auditors.
By Jenny ShenJuly 22, 2024 -
HIPAA
IT Risk Assessment and HIPAA Compliance
Get an IT Risk Assessment by the experts at Linford and Company, for greater HIPAA compliance and better protection against data breaches and OCR audits.
By Jenny ShenMay 20, 2024 -
HITRUST
What are HITRUST® Correction Action Plans (CAPs)? Answers to Common Questions
What is a HITRUST Correction Action Plan (aka CAP)? Here are some commonly asked questions on what you need to know, answered by a HITRUST External Assessor.
By Jenny ShenOctober 26, 2022 -
Compliance
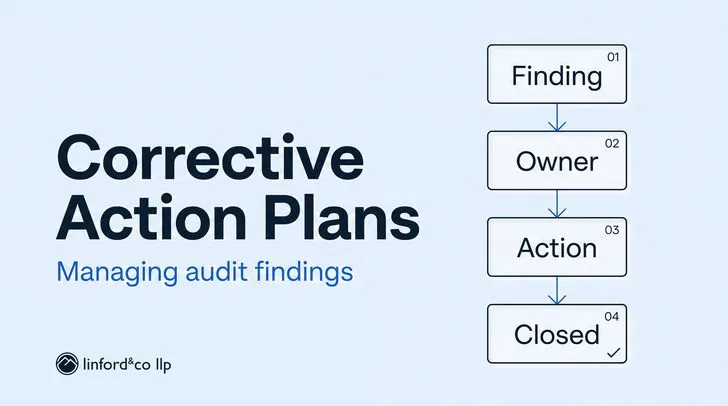
Corrective Action Plans 101: Guide for Managing Audit Findings
What is a corrective action plan? Here's professional guidance on the purpose, process, how to create a plan to manage audit findings, and achieve compliance.
By Jenny ShenMay 11, 2022 -
SOC 2
What is a Security Operations Center (SOC) & Why Should You Invest in One?
What is a Security Operations Center and could it affect your organization? Here's a breakdown of how they work, what the benefits are, and why to invest in one.
By Jenny ShenJanuary 5, 2022
Get in touch
Have a question an article didn't answer? Talk to a partner.
Get straightforward answers from experienced auditors.