Articles
-
AI & Emerging Risk
CSA STAR for AI & ISO/IEC 42001: Which Should You Choose?
Companies that use AI as part of their daily practices, and customers of providers that use AI in their business model, are asking which assurance fits best.
By Lois ColbyAugust 12, 2026 -
ISO
Performing CSA-STAR Certification Audit in Conjunction with ISO/IEC 27001
Combining CSA STAR Level 2 with ISO 27001? Discover what you need to know about maturity scoring, CAIQ requirements, and integrated audit planning.
By Lois ColbyFebruary 18, 2026 -
Compliance
What Is an Unqualified Opinion Versus Other Report Opinions?
Learn what an unqualified audit opinion means for SOC 1 and SOC 2 reports, how it differs from qualified opinions, and why it's the gold standard.
By Lois ColbyJuly 16, 2025 -
CMMC & NIST
Guide To Creating a CMMC Compliant System Security Plan (SSP)
Learn how to create a System Security Plan (SSP) for CMMC Level 2 certification, including scope determination, components, and maintenance best practices.
By Lois ColbyApril 30, 2025 -
Compliance
AICPA Quality Management Standard (SQMS) No. 1 (and Why You Should Care)
Learn about the new AICPA Quality Management Standard (SQMS) No. 1, its importance for CPA firms, plus how it impacts attestation services like SOC 1 & SOC 2 reports.
By Lois ColbySeptember 25, 2024 -
SOC 2
SOC 3 Reports: Do You Need One?
The SOC 3 report is a general-use report after an attestation examination is conducted in accordance with the SSAE 18 standard. But who needs one?
By Lois ColbyMay 21, 2024 -
CMMC & NIST
What is the CMMC (2.0)? New DoD Guidance for Security Compliance
What is the CMMC? This in-depth guide provides clarity on cybersecurity model maturity certification, including recent updates that could affect your DoD contracts.
By Lois ColbyApril 24, 2024 -
SOC 1
Critical Audit Matters (CAMs) & SOC 1 Reports - Could They Be Related?
What are critical audit matters (CAMs) and how are they related to your SOC 1 report? Learn how an exception or qualification may be a contributing factor.
By Lois ColbyNovember 15, 2023 -
AI & Emerging Risk
SOC 2 Audit Considerations for AI & ML Subservice Organizations
More & more subservice organizations are providing artificial intelligence & machine learning services. How are they audited? Here are SOC 2 considerations.
By Lois ColbyJuly 5, 2023 -
SOC 2
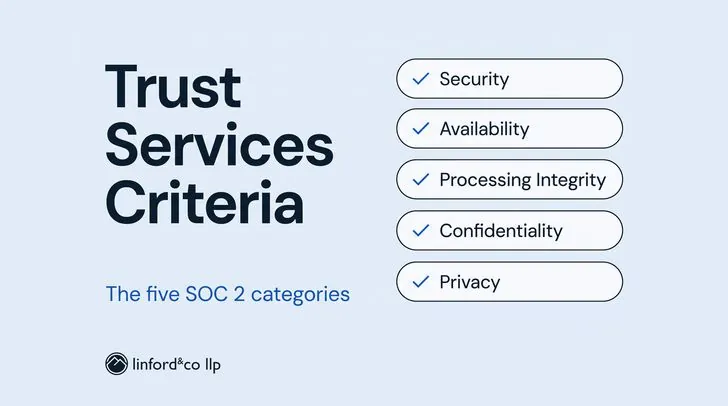
Trust Services Criteria (TSCs) for SOC 2 Reports
What are the AICPA Trust Services Criteria (f. Principles)? How do they relate to your SOC 2 audit? Here is recently updated guidance and what you should know.
By Lois ColbyFebruary 1, 2023 -
SOC 1
SSAE-21: New AICPA Guidance for Assertion-Based & Examination Engagements
In September of 2020, the AICPA came out with SSAE-21, which outlines new guidelines for assertion-based and examination engagements. Here is the breakdown.
By Lois ColbySeptember 14, 2022 -
SOC 1
Audit Trails for the SOC 1/SOC 2 Audit & Investigative Processes
What are audit trails? Learn more about how they are critical to the everyday operations of your organization, as well as documentation for the audit process.
By Lois ColbyApril 27, 2022
Get in touch
Have a question an article didn't answer? Talk to a partner.
Get straightforward answers from experienced auditors.