Articles, page 14 of 28
-
HIPAA
HIPAA Authorization: Requirements & Consent for Disclosing PHI
Covered entities, under the Privacy Rule, cannot disclose protected health information without patient consent. Learn about HIPAA Authorization Requirements.
By Jaclyn FinneyDecember 27, 2023 -
SOC 2
Pitfalls to Avoid When Transitioning From a Type I to a Type II SOC Report
Learn from the mistakes of others and avoid these 5 common pitfalls when transitioning your organization from a Type I to a Type II SOC Report.
By Kevin AndersonDecember 20, 2023 -
Compliance
Access Control Issues - Principles for Success & Avoiding Common Pitfalls
Issues with access control can directly impact the outcome of an audit. Here is professional insight on some common pitfalls to avoid & principles for success.
By Tim NackosDecember 13, 2023 -
Compliance
A Guide to Microsoft’s Supplier Security Privacy Assurance (SSPA) Program
This guide breaks down Microsoft's Supplier Security Privacy Assurance (SSPA) program - what it is, and the requirements for compliance and audit assurance.
By Mark LarsonNovember 29, 2023 -
HITRUST
A Guide to HITRUST® Interim Assessments
This guide explains the ins and outs of a HITRUST interim assessment - what it is, when it is needed, if one can be completed, the timeline, and what to expect.
By Brian SandenawNovember 22, 2023 -
SOC 1
Critical Audit Matters (CAMs) & SOC 1 Reports - Could They Be Related?
What are critical audit matters (CAMs) and how are they related to your SOC 1 report? Learn how an exception or qualification may be a contributing factor.
By Lois ColbyNovember 15, 2023 -
Compliance
Business Continuity vs. Disaster Recovery: The Building Blocks for Preparation
What is business continuity vs disaster recovery? We break down the differences between these recovery plans, as well as when & why they should be implemented.
By Hilary StavrakasOctober 11, 2023 -
HITRUST
What is HITRUST®? A Comprehensive Guide to HITRUST Assessments
What is HITRUST? Why is it important? This guide covers the benefits, requirements, who needs certification, how it compares to other frameworks, & more.
By Richard RiebenOctober 4, 2023 -
AI & Emerging Risk
Enhancing Your Company’s AI Security Policy - Professional Insights
As the use of AI continues to grow, it has become crucial to implement an AI security policy. Here are insights on what to consider and why it's important.
By Ben BurkettSeptember 27, 2023 -
ISO
ISO Certificate Verification: Considerations & Guidance
ISO certification is necessary for the standardization & quality assurance of an organization. This guide explains what to look for to verify its validity.
By Rhonda WillertSeptember 20, 2023 -
Compliance
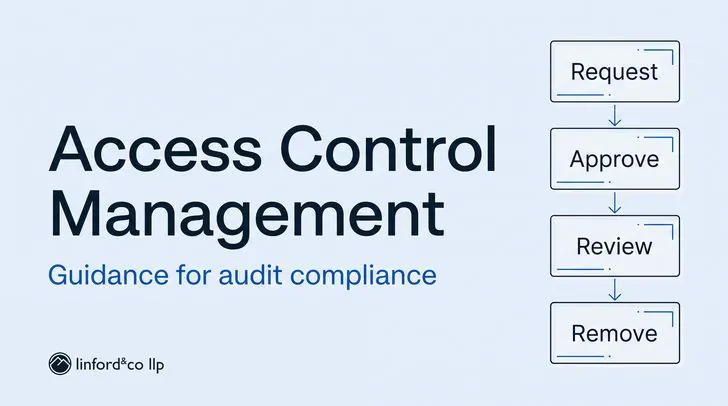
Access Control Management - Guidance for Audit Compliance
What are access management controls & how do they affect your internal control environment? We cover types & examples of access controls, IAM tools, & benefits.
By Megan KovashSeptember 13, 2023 -
Compliance
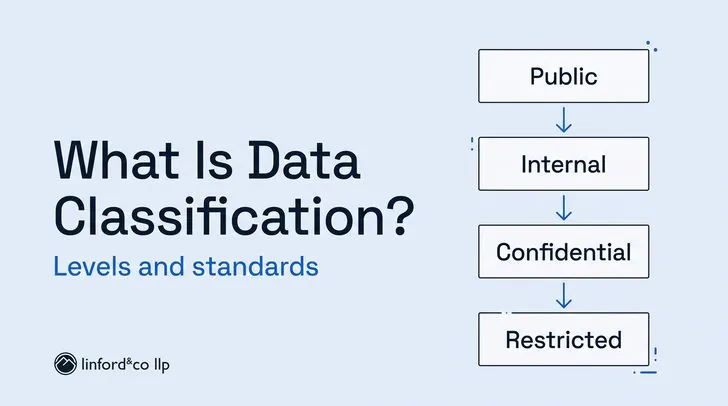
What is Data Classification? Levels, Compliance, & Standards to Follow
When it comes to compliance, data classification is critical. This includes understanding how data should be maintained & protected within your organization.
By Maggie CheneyAugust 30, 2023
Get in touch
Have a question an article didn't answer? Talk to a partner.
Get straightforward answers from experienced auditors.