A few months ago I got a call from a company that was certain it needed a SOC 1 report. Their largest customer had asked for one, the sales team had promised it, and the CFO wanted to know how fast we could start. Ten minutes into the conversation, I asked the question I ask almost every time: Can your service impact the financial statements of your clients?
There was a long pause. Then the CTO said, “We host their data, and they run reports out of it, but we can’t change anything.”
That answer told me they probably did not need a SOC 1. They needed a SOC 2. Their platform gave clients a different view of data the clients themselves owned and controlled. It was read access. No transactions were created, no balances were calculated, no dollars moved. If their system went down on a Tuesday, nobody’s general ledger was wrong on Wednesday.
That conversation happens more often than you would think, and it is the reason this article exists. If you are trying to figure out what a SOC 1 report is, whether you need one, and what you are signing up for, here is what I have learned from performing these examinations.
What Is a SOC 1 Report & Who Can Perform One?
A SOC 1 report is an audit report whose scope includes both business process and information technology control objectives and testing. It must be issued by a CPA firm that specializes in auditing IT and business process controls. SOC 1 reports are attestation reports, not certifications, which is why the phrase “SOC 1 certification” is technically incorrect even though you will see it used everywhere.
In a SOC 1, management asserts that certain controls are in place to meet the control objectives included in the report. The CPA firm then tests controls related to management’s assertion and provides an opinion on whether it agrees with that assertion. The report is tailored to the service organization receiving it, and there is no standard set of requirements tested. That last point surprises people constantly.
I once had a first-time client email me two days after our kickoff call asking me to send over “the SOC 1 checklist.” They had been through a SOC 2 readiness effort the year before and assumed there was an equivalent list of predefined requirements. There is not. A SOC 2 has the Trust Services Criteria, which are published and fixed. A SOC 1 has control objectives that you and your auditor write together based on what your service actually does and what could go wrong. That is more freedom and more work at the same time.
A SOC 1 report includes an auditor’s opinion that is either qualified or unqualified. An unqualified SOC 1 report is what most people call a “clean” report. A qualified report includes language in the opinion letter that describes the qualification and identifies one or more control objectives that were not met. If you want more on what a qualification actually looks like in practice, we have written about qualified audit reports and SOC opinions separately.
What Are SOC 1 Control Objectives?
Control objectives are the aim or purpose of the controls within a SOC 1 process area. Think of them as overarching statements for each process area in the report. They should address the risks that the controls in that area are intended to mitigate.
A sample control objective might read:
Controls provide reasonable assurance that logical and physical access to programs, data, and computer resources relevant to user entities’ internal control over financial reporting is restricted to authorized and appropriate users, and such users are restricted to performing authorized and appropriate actions.
In that example, the auditor and the service organization work together to identify the controls that support the statement. Supporting controls could include password requirements, multi-factor authentication, role-based access enforcement, and physical security at the facility.
Here is where new clients get tangled up. Early in one engagement, the client’s compliance lead sent me a spreadsheet with about sixty controls on it and asked which objectives they mapped to. It was a reasonable instinct and exactly backwards. Objectives come first. You define what has to be true, then you identify the controls that make it true. When you start from a pile of controls and work upward, you end up with objectives that describe what you happen to be doing rather than what your clients’ financial reporting actually depends on.
Below is how control objectives, controls, and risks typically line up in a SOC 1:
| Control Objective Area | Example Controls | Risk Addressed |
| Logical access | User access provisioning and approval, quarterly access reviews, multi-factor authentication, timely termination of access | Unauthorized users view or alter financially relevant data |
| Change management | Change request and approval workflow, segregated development and production environments, testing before release | Untested or unapproved code changes corrupt financial processing |
| Computer operations | Job scheduling and monitoring, failed job escalation, backup and restoration testing | Processing failures go undetected and financial data is lost or incomplete |
| Physical and environmental security | Badge access to data centers, visitor logs, environmental monitoring | Physical compromise of systems supporting client financial reporting |
| Transaction processing | Input validation, exception reporting and resolution, automated calculation checks | Transactions are processed inaccurately, incompletely, or without authorization |
| Reconciliation and reporting | Daily or monthly reconciliations, supervisory review and sign-off, client reporting accuracy checks | Errors reach client financial statements undetected |
Notice the “reasonable assurance” language. It is consistent across SOC 1 control objectives, and it matters more than most people realize. The auditor is not providing absolute assurance that objectives are met.
I had a client call me in a genuine panic during fieldwork because one of their quarterly access reviews had not been completed on time. They were convinced the report was going to be qualified and that they would lose an account over it. It was not, and they did not. Other controls in that process area were designed and operating well enough that the objective was still met at the reasonable assurance level. That is not a loophole. It is how the standard is built. Controls fail. The question is whether the remaining controls carry the objective.
That said, do not read this as permission to let controls slip. Each control objective must have enough controls designed and operating effectively in a Type II SOC 1 to support the objective statement without qualification. There is a floor, and it is not always obvious where it is until you are in the middle of testing.
What Is a SOC 1 Report Used For?
SOC 1 reports let the financial statement auditors of user entities place reliance on processes performed by service organizations. Instead of auditing your controls themselves, your client’s auditor reads your SOC 1 and relies on the work already performed.
This is the part that determines your deadline, and it is where I see the most avoidable pain. One client learned in late January that their customer’s external audit team needed a SOC 1 covering the prior calendar year, and needed it in about three weeks. There was no report, no prior-year baseline, and no evidence retained for a twelve-month period. We could not manufacture history. They ended up with a Type I as of a date in the current year and a commitment to a Type II the following year, which their customer accepted but was not thrilled about.
If your clients are audited companies, ask them when their audit fieldwork happens. That answer should drive your examination period end date, not the other way around.
What Are Service Organizations & User Entities?
“Service organization” is the AICPA’s term for a company that other companies outsource work to. A service organization supports processes its clients have handed off. The long-running trend toward outsourcing has put a lot of financially relevant processes in the hands of third parties.
Payroll is the cleanest example. Rather than run payroll internally, a company outsources it to a provider like ADP or Paychex. In that relationship, the provider is a service organization that can absolutely impact the financial statements of its clients. If the provider miscalculates withholding or misses a payroll run, that error lands in someone else’s books.
User entities are the consumers of SOC 1 reports. They are typically the companies that outsourced part of their internal control over financial reporting to a service organization. User entities can also be investors or the external auditors of companies using those service organizations.
One nuance worth flagging: your report will likely include complementary user entity controls, which are the things your clients have to do on their end for your controls to work. Clients often skim past this section when drafting. Your users’ auditors do not. We have covered complementary user entity controls and considerations in more depth if you are writing that section for the first time.
Are SOC 1 Reports Mandatory? Who Needs One?
No law requires a SOC 1 report. In practice, your clients or investors require one when your service can impact their internal control over financial reporting (ICFR).
Whether you get asked depends on your industry and on the risk associated with what you do. A SOC 1 demonstrates that you have IT general controls as well as business process controls such as reconciliations and transaction authorizations supporting your control objective statements. Organizations that commonly receive SOC 1 reports include:
- Payroll processors
- Medical claims processors
- Loan servicing companies
- Data center and colocation companies
- Trust and custody providers
- Benefits administrators
- Software-as-a-service companies whose platforms calculate, record, or move amounts that land in client financial statements
The common thread is potential impact on user entities’ ICFR. It is not about how sensitive your data is. It is about whether you can put a wrong number in someone else’s ledger.
How Do You Know If You Can Impact Your Clients’ ICFR?
Here is the test I walk prospects through on the first call. Ask yourself whether your service does any of the following:
- Creates, calculates, or posts transactions that flow into a client’s financial records
- Holds or moves client funds
- Produces reports or data files that clients use directly to prepare financial statements
- Maintains records that a client relies on for revenue recognition, payables, receivables, or payroll
- Performs a reconciliation or approval step that would otherwise be performed inside the client’s own accounting function
If the honest answer to all five is no, you are probably looking at a SOC 2 rather than a SOC 1. If the answer to any of them is yes, keep going.
Scoping is its own conversation. I worked with a company that assumed the entire organization would be in scope because that is how their SOC 2 had worked. In reality, only one of their four product lines touched client financial data. The other three were operational tools. Scoping the SOC 1 to that single product line and its supporting infrastructure cut the effort significantly and made the report more meaningful to the people reading it. Broader is not better in a SOC 1. Relevant is better.
SOC 1 Type I vs. Type II: Which Report Do You Need?
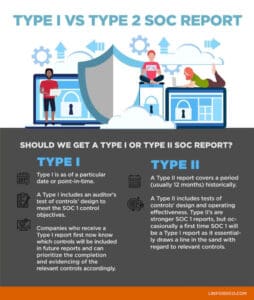
A Type I report covers a particular date or point in time. A Type II report covers a period, usually twelve months, in the past. A Type I includes the auditor’s test of the design of controls to meet the SOC 1 control objectives. A Type II includes tests of both design and operating effectiveness.
Type II reports provide greater assurance, and most user entities want them. Occasionally a first-time SOC 1 is a Type I, and there is a good argument for that path. A Type I essentially draws a line in the sand. Once you have one, you know exactly which controls will be tested going forward, and you can prioritize evidence retention accordingly.
I have watched both approaches play out. One client insisted on a Type II for their first report because their customer had asked for one. Three weeks into fieldwork, it became clear that the quarterly access reviews had only been performed once during the period and that change tickets from the first four months were in a system they had since migrated away from. We converted the engagement to a Type I. Another client in a similar position started with a Type I on purpose, spent the following year running the controls with evidence in mind, and their Type II the next year was one of the smoother examinations I have been part of.
If you have not been operating and documenting controls consistently for the full period, a Type II will find that out. There is more detail in our article on SOC report types.
SOC 1 vs. SOC 2 vs. SOC 3
The short version:
- SOC 1 addresses controls relevant to user entities’ internal control over financial reporting. Control objectives are custom to your organization. The audience is your clients and their financial statement auditors.
- SOC 2 addresses controls relevant to security, availability, processing integrity, confidentiality, and privacy, tested against the predefined Trust Services Criteria. The audience is clients, prospects, and security teams evaluating your controls.
- SOC 3 covers the same subject matter as a SOC 2 but is a short, general-use report with no detailed description of tests and results. It is the version you can post on your website.
Plenty of organizations end up needing both a SOC 1 and a SOC 2, particularly SaaS providers whose platforms are both security sensitive and financially relevant. We cover the comparison in more detail in SOC 1 vs. SOC 2 and SOC 2 vs. SOC 3.
What Does SOC 1 Compliance Mean?
SOC 1 compliance means maintaining the controls included in your SOC 1 report over time. You will also hear it described as maintaining the operating effectiveness of your SOC 1 controls. Those controls are the IT general controls and business process controls needed to demonstrate reasonable assurance against your control objectives.
The failure mode I see most often is not a bad control design. It is a good control that stops being performed in month seven because the person who owned it changed roles and nobody picked it up. Type II testing samples across the whole period, so a control that ran beautifully for six months and then quietly stopped will surface. Assigning a named owner and a backup to every control is worth more than most compliance tooling.
How Long Is a SOC 1 Report Valid and How Often Is It Issued?
Type II SOC 1 reports cover a period of time in the past, for example, January 1 through December 31, 2026. The typical examination period is twelve months, though Type II periods range from six to eighteen months.
Some firms issue Type II reports covering shorter periods. The concept of a Type II is to demonstrate operating effectiveness over time, so if the window is too short, it starts to resemble a Type I with extra steps.
Most service organizations issue a report annually on a consistent period so their clients’ auditors can rely on continuous coverage. When a report is issued late or the period shifts, user entities are left with a gap, and gaps generate questions. A bridge letter can cover a short stretch between the period end and the client’s year-end, but it is not a substitute for a report, and it carries no auditor opinion.
How Much Does a SOC 1 Audit Cost?
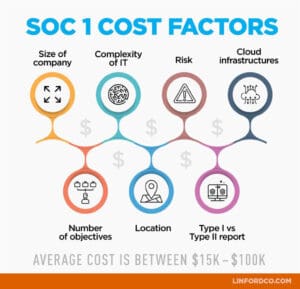
Examination fees vary. The factors audit firms weigh include:
- Size of the company and number of individuals with in-scope system access
- Complexity of the IT and business process control environment
- Risk associated with the services provided and the data stored
- Use of cloud infrastructure such as AWS, Azure, or GCP
- Number of business process control objectives
- Number and location of offices and data centers in scope
- Type I versus Type II
The number of business process control objectives is the one people underestimate. IT general controls tend to look similar across organizations. Business process objectives are where the work lives, and a scoping conversation that trims two unnecessary process areas will do more for your fee than any amount of negotiating.
How Do You Prepare for a SOC 1 Audit?
Considerations for organizations approaching a first SOC 1:
- Define the services and systems that actually touch client financial reporting before anything else. Scope drives everything downstream.
- Draft your control objectives with your auditor early, not after you have written control descriptions.
- Assign an owner and a backup to every control.
- Decide where evidence lives and retain it from day one of the period. Screenshots taken retroactively are not evidence of a control operating in March.
- Identify your subservice organizations and decide whether you are carving them out or including them.
- Write your complementary user entity controls honestly and share them with your account teams so nobody promises clients something the report contradicts.
- Work backward from your clients’ audit calendars to set your period end date.
SOC 1 Report FAQs
A few questions come up on nearly every SOC 1 call I take. Here are the quick answers.
What Does SOC 1 Stand For?
SOC stands for System and Organization Controls. The 1 designates the report focused on controls relevant to user entities’ internal control over financial reporting.
Is a SOC 1 Report the Same as SAS 70 or SSAE 16?
Not the same, but related by lineage. SAS 70 was replaced by SSAE 16, which was superseded by SSAE 18. The report itself is now called a SOC 1. The history is covered in our article on what SAS 70 is called now.
Who Prepares a SOC 1 Report?
Management prepares the system description and the assertion. A licensed CPA firm performs the examination and issues the opinion.
Is There Such a Thing as SOC 1 Certification?
No. A SOC 1 is an attestation report, not a certification, and there is no certifying body issuing a SOC 1 credential.
How Do You Obtain a SOC 1 Report from a Vendor?
Ask your account representative directly. Most service organizations will provide the report under a nondisclosure agreement. If a vendor cannot produce one and their service touches your financial reporting, that itself is useful information.
Are SOC Reports Public?
SOC 1 and SOC 2 reports are restricted use and are shared under NDA. SOC 3 reports are general use and can be published openly.
How Long Does a SOC 1 Audit Take?
Fieldwork for a Type II is commonly four to eight weeks, depending on scope and how quickly evidence arrives. The period being examined is separate and is usually twelve months.
Is a SOC 1 or a SOC 2 Better?
Neither. They answer different questions. The right report is the one your clients and their auditors actually need.
What Is a SOC 1 Checklist?
There is no standard checklist, because control objectives are tailored to the service organization. The closest equivalent is the set of objectives and controls you and your auditor agree to during scoping.
Can a SOC 1 Report Say Anything About Future Control Performance?
No. A SOC 1 speaks to a point in time or a period in the past. It makes no statement about how controls will perform going forward.
The Bottom Line on SOC 1 Reports
Your company may be required to get a SOC 1 report by clients or stakeholders. SOC 1 reports cover the business process control objectives and IT general controls that address the risks your users take on by using your service. A SOC 1 is the right report if your service is relevant to, or could impact, the financial statements of your clients. It can be a Type I as of a particular date or a Type II covering a period in the past, and it cannot include any statement about future control performance.
If I could get one point across, it would be the one from that first phone call. Holding client data is not the same as impacting client financials. Answer that question honestly before you commit to a report type, because getting it wrong costs a year.
If your company needs to go through a SOC 1 examination, choose your auditor carefully. Some firms dabble in SOC 1 examinations alongside tax and bookkeeping work. Linford and Company specializes in performing SOC 1 examinations for small to large-sized businesses. Please feel free to contact me with any SOC 1-related questions.
This article was originally published on 11/22/2017 and was updated on 4/12/2023 and 9/9/26.