IT Audit & Compliance Blog

The Linford & Company Blog is written by our very own auditors, who are experts in IT audits, information security, and compliance topics. Their auditing experience encompasses a broad spectrum of industries and organizations, and their specialized expertise can help your company or organization make the right decision for your auditing needs. Our specific areas of focus in our IT Audit & Compliance Blog include SOC 1 Audits, SOC 2 Audits, HIPAA Audits, HITRUST Certification, and FedRAMP Assessments, NIST & CMMC, and Penetration Testing.

Whether for an agency assessment or a Joint Authorization Board (JAB) assessment, the FedRAMP System Security Plan (SSP) is the foundational document that supports a FedRAMP assessment. From it, the government agency representatives and the Third Party Assessment Organization (3PAO) are able to get an understanding of how the FedRAMP baseline security controls are implemented [...]

Having a plan in place to backup pertinent information to keeping a business running in the event information becomes unavailable for use is an important concept of business continuity. This blog will provide a definition and importance of corporate data backups, outline solutions options, and define best practices used for defining a corporate data backup [...]

How Long Does a SOC Examination Take?

By Nicole Hemmer Published on December 13, 2017
We are frequently asked how long it takes to complete a SOC examination. Unfortunately there is not an answer that fits for every examination because every service organization is different. But, if an organization has controls in place the average time taken for a SOC examination is typically one to three months for Type I [...]

Today’s information environments are always changing, whether through the development of new capabilities, patching systems, responding to new threats and vulnerabilities, or fixing discrepancies within the system. Each change to the system carries with it an inherent security risk. Therefore, that security risk must be evaluated in the context of the security posture of the [...]

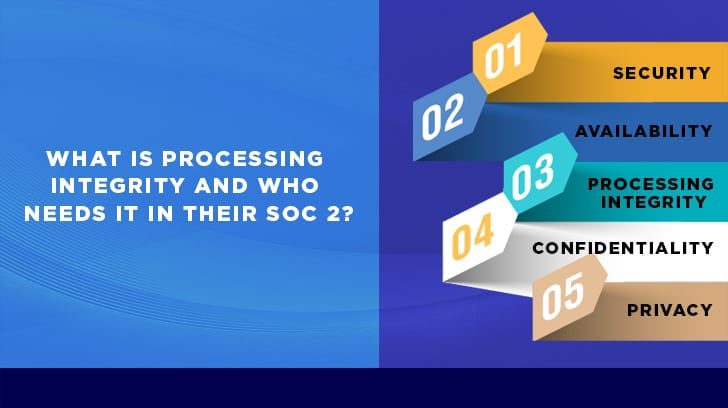
There are five trust services criteria that can be included in a SOC 2 report, including: security, availability, processing integrity, confidentiality, and privacy (see definitions from the AICPA below). Only one of the five criteria is required in the SOC 2 — security. The other four trust services criteria are optional, and we get many [...]

Risk management is a basic component of everything we do. Subconsciously, we assess and manage risk with each decision we make—from getting up in the morning to going back to sleep. So, in a way, most of us are already seasoned risk managers. Yet many find organizational risk management to be an overwhelming task. Managing [...]

Is the Cloud Safe?

By Jaclyn Finney Published on July 12, 2017

More and more companies are popping up that require their consumers to insert sensitive information into a cloud for safe keeping but is the cloud actually safe? This article will address that question and provide consumers some insight into steps they can take and what to look for to help ensure that their information is [...]

The AICPA has recently developed a cybersecurity risk management reporting framework that is being added to the suite of System and Organization Controls (SOC) report offerings. This framework will assist organizations in communicating relevant and useful information about their cybersecurity risk management program. Companies need to be able to evidence that they can manage cybersecurity [...]

No Matches Found

But there’s still plenty worth exploring. Try a different search, or browse the Blog.

"*" indicates required fields

This field is for validation purposes and should be left unchanged.
I understand and agree to the Linford & Company LLP privacy policy.**