One assessment, many agencies
An authorization from one agency, or from the GovRAMP PMO, can be leveraged across many participating state and local government agencies.
GovRAMP Assessments
Independent assessments from an A2LA-accredited 3PAO to help cloud service providers achieve GovRAMP authorization and expand their reach in state and local government.
GovRAMP was formerly known as StateRAMP.
The GovRAMP journey
The entry point. The Progressing Security Snapshot is a structured 40-control maturity assessment, and providers are listed on GovRAMP's Progressing Product List.
The first verified status. The GovRAMP PMO reviews evidence that 60 foundational controls, aligned to the NIST SP 800-53 Rev. 5 Moderate baseline, are in place, along with 90 days of continuous monitoring data.
An accredited 3PAO attests that you meet the minimum security standards for your impact level.
After a full assessment, you receive an Authorization to Operate from a state or local agency, or from the GovRAMP PMO.
Core, Ready, and Authorized are GovRAMP's verified security statuses. Your target status depends on your agency customers and your system's impact level.
Why it matters
An authorization from one agency, or from the GovRAMP PMO, can be leveraged across many participating state and local government agencies.
The assessment examines people, processes, and technology across your cloud environment against a control framework agencies already trust.
FedRAMP recognizes GovRAMP as an approved alternative security framework for 20x Class A. A GovRAMP assessment completed within the past 12 months meets the Class A prerequisite. Class B and C require their own 20x assessment.
GovRAMP and FedRAMP
GovRAMP and FedRAMP serve different buyers, and FedRAMP now has two paths of its own. Here is how GovRAMP work carries over to each.
| GovRAMP | FedRAMP 20x Open | FedRAMP Rev5 Closing | |
|---|---|---|---|
| Buyers | State and local government agencies | Federal agencies | Federal agencies |
| Basis | NIST SP 800-53 plus GovRAMP-specific control enhancements | Key Security Indicators and FedRAMP rules | NIST SP 800-53 Rev. 5 baselines plus FedRAMP enhancements |
| Evidence | Documentation review, interviews, and technical testing | Automated, machine-readable validation, and historical metrics | Documentation review, interviews, and technical testing |
| Assessor deliverables | Security Assessment Plan and Security Assessment Report | Assessment summaries for the Security Decision Record and Certification Package | SAP, test case workbooks, Risk Exposure Table, and SAR |
| Program office | GovRAMP PMO and agency sponsors | FedRAMP PMO | FedRAMP PMO and agency sponsors |
| How GovRAMP work carries over | FedRAMP recognizes GovRAMP as an approved alternative security framework for Class A. A GovRAMP assessment from the past 12 months meets the prerequisite, with your GovRAMP RAR or SAR as supporting documentation. Class B and C need their own 20x assessment. | Same control framework, but the FedRAMP PMO stops accepting new traditional Rev5 applications on June 11, 2027. |
Planning for federal buyers too? See our FedRAMP assessments page to compare the 20x and Rev5 paths.
Our assessment process
We meet with your management and technical staff to understand your requirements, boundary, and timeline.
With the GovRAMP PMO and your agency sponsor, we set milestones and develop the Security Assessment Plan (SAP).
We request and review your documentation, policies, and system evidence.
Interviews and technical testing against NIST SP 800-53 and GovRAMP controls, including penetration testing.
We walk through results and any findings with you before the report is finalized.
The Security Assessment Report (SAR), reviewed with you before it is submitted.
We respond to questions from the GovRAMP PMO and agency reviewers about our assessment. Annual assessments follow your authorization.
What you receive
GovRAMP requires two assessor deliverables, plus an optional readiness report if you choose one. We review the results with you before anything goes to an agency or the GovRAMP PMO.
SAP
The scope, approach, and schedule for the assessment, agreed with you, the GovRAMP PMO, and your agency sponsor.
SAR
Our results and any findings, reported to you, your agency sponsor, and the GovRAMP PMO.
RAR · Optional
If you choose a readiness assessment, we prepare and submit the RAR. It is not required for GovRAMP.
Our partners
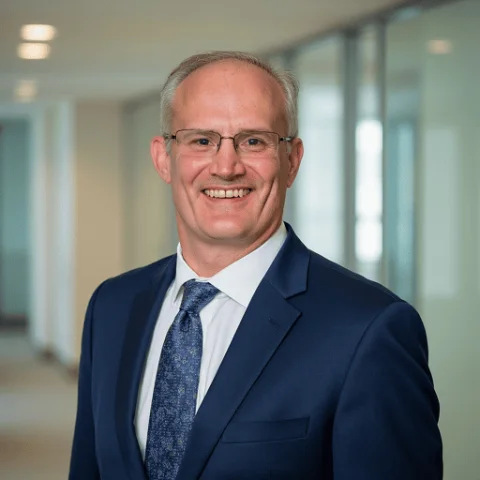
Partner
CISSP, CISA, GSEC, GWAPT
Performs our FedRAMP and GovRAMP assessments. Former Air Force communications and computer systems officer with a background in defense-industry security engineering.
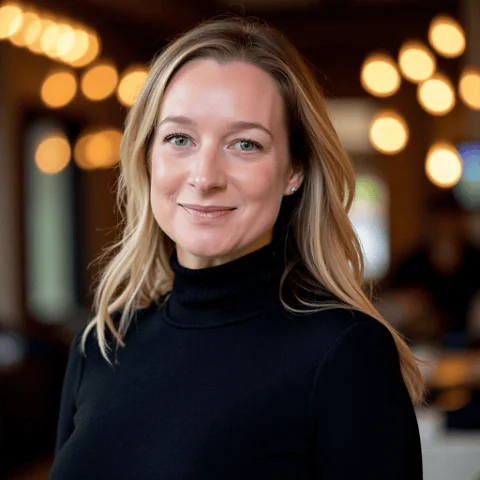
Partner
CISA, ISO 27001 Lead Auditor
Partner with a special focus on SOC, ISO, and FedRAMP examinations, tailoring each assessment to the client.
A2LA accredited
Linford & Company is an A2LA-accredited, authorized GovRAMP 3PAO and a FedRAMP Recognized Independent Assessment Service.
View our accreditationFrequently asked questions
The Government Risk and Authorization Management Program (GovRAMP), formerly StateRAMP, was formed in 2021 to help state and local governments manage third-party risk in commercial cloud environments. It was modeled on the traditional FedRAMP approach, with a standardized way to verify the security of cloud services against NIST SP 800-53.
Cloud service providers that want to sell to state and local governments. You will need to show compliance with NIST SP 800-53 and GovRAMP-specific security controls.
An independent Third Party Assessment Organization (3PAO) accredited by A2LA. Linford & Company is an authorized GovRAMP 3PAO.
GovRAMP requires two assessor deliverables: the Security Assessment Plan (SAP) and the Security Assessment Report (SAR). If you choose a readiness assessment, we also prepare and submit a Readiness Assessment Report (RAR); it is optional. We review the results with you before anything goes to an agency or the GovRAMP PMO.
GovRAMP serves state and local government buyers, with its own program office and control enhancements. FedRAMP serves federal agencies and now has two paths. The traditional Rev5 path shares GovRAMP's NIST SP 800-53 foundation, but the FedRAMP PMO will stop accepting new traditional Rev5 applications on June 11, 2027. The newer FedRAMP 20x path uses Key Security Indicators and automated validation instead. A GovRAMP assessment completed within the past 12 months meets the prerequisite for 20x Class A.
For FedRAMP 20x Class A, yes. FedRAMP's updated Class A Certification Rules recognize GovRAMP as an approved alternative security framework. A GovRAMP assessment completed within the past 12 months satisfies the Class A prerequisite, and your GovRAMP Readiness Assessment Report (RAR) or Security Assessment Report (SAR) serves as supporting documentation. This does not change FedRAMP's certification requirements; you still need to meet all applicable FedRAMP rules. For Class B and C, FedRAMP requires its own 20x assessment. GovRAMP's Federal Overlay, which compares GovRAMP Low, Moderate, and High baselines with federal requirements, shows where additional work may apply.
GovRAMP assessments take real time and effort. We gather what we need efficiently, to keep the impact on your day-to-day operations as small as possible.
Ready to make a bigger impact?
Talk with a partner about your GovRAMP assessment and the agencies you want to serve.