Articles, page 13 of 28
-
AI & Emerging Risk
Risk Management in the Era of Large Language Models and Generative AI
Large Language Models & Generative-AI platforms are changing the landscape of business. We cover security concerns and how to effectively manage your risk.
By Richard RiebenApril 10, 2024 -
Compliance
Zero Trust Implementation - Guidelines & Best Practices
Implementing a zero trust security model doesn't have to be intimidating. This guide covers each step of the process and tools to help maintain compliance.
By Umar AzizApril 3, 2024 -
SOC 2
Cloud Patch Management Importance & Impact on SOC Reports
What is cloud patch management? This guide discusses how it can impact your organization and provides step-by-step guidance for SOC audit compliance.
By Britney OswaldMarch 20, 2024 -
HIPAA
HIPAA Business Associate vs. Covered Entity: Differences & Expectations
What is a covered entity and how does it differ from a HIPAA business associate? This breakdown explains who is and isn't covered, who needs them, and more.
By Hilary StavrakasMarch 13, 2024 -
Compliance
Audit Readiness: Professional Tips for a Successful Audit
This guide to audit readiness provides professional insights into how to best prepare for your organization's upcoming audit, and what to avoid.
By Danielle PeiMarch 6, 2024 -
SOC 2
Myth Busting 5 Common SOC Audit Misconceptions
This article breaks down the most common misconceptions we come across as auditors when clients are preparing for an upcoming SOC audit. Here are the facts.
By Ben BurkettFebruary 28, 2024 -
Penetration Testing
Which Types of Vulnerability Scanners Can Help Protect Your Company?
There are several different types of vulnerability scanners, so how do you decide which one (or more) is right for your organization? Here is guidance to help.
By Jessica KielFebruary 14, 2024 -
Compliance
Zero Trust Concepts & Audit Implications
What is Zero Trust? Here is our comprehensive guide on Zero Trust concepts and their critical role in enhancing audit processes and governance frameworks.
By Richard RiebenFebruary 7, 2024 -
SOC 2
Navigating SOC 2 Scope for a Successful Audit - Professional Insights
Confused about SOC 2 audit scope? These insights will help you understand how to tailor an audit scope to meet your security, compliance, and business needs.
By Megan KovashJanuary 24, 2024 -
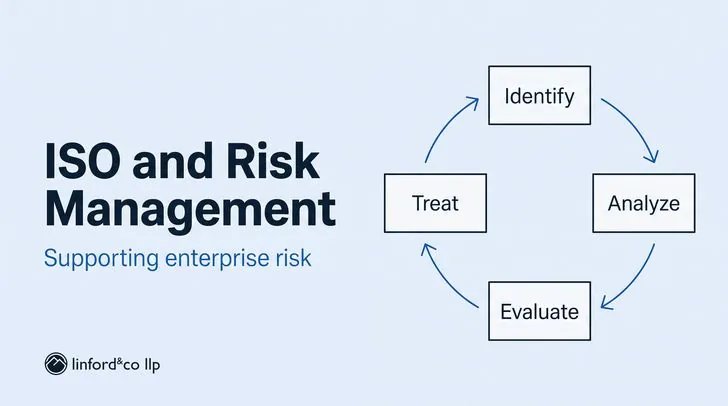
ISO
ISO and Risk Management Frameworks for Supporting Enterprise Risk Assessments
This breakdown compares several risk management frameworks, including ISO 31000 - similarities, differences, benefits, & why it's critical to your organization.
By Rhonda WillertJanuary 17, 2024 -
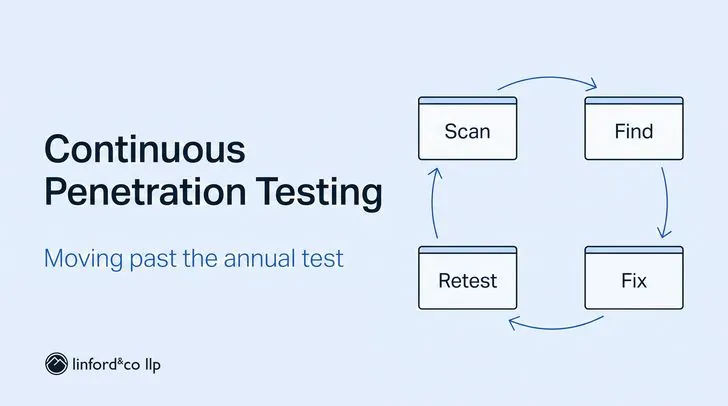
Penetration Testing
Stop Pen Testing Like It’s Y2K - How to Implement Continuous Penetration Testing
This breakdown explains why implementing continuous penetration testing is more effective than the annual model, including benefits, cost, & why it's important.
By L&Co Staff AuditorsJanuary 10, 2024 -
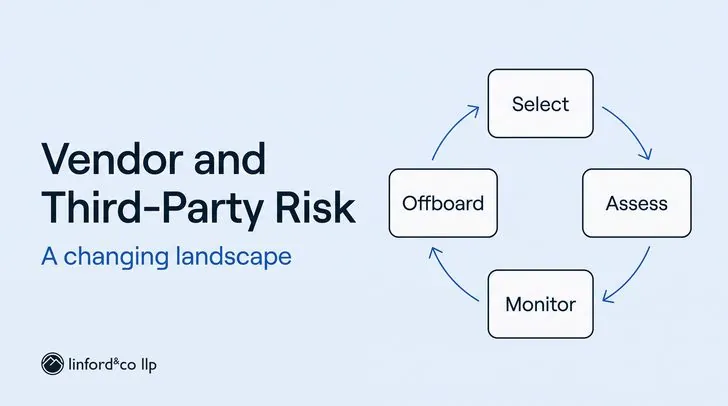
Compliance
The Transforming Landscape of Vendor & Third-Party Risk Management
Here is a breakdown of the vendor & third-party risk management process - from guidance for sharing data to monitoring & best practices for your organization.
By John PohlmannJanuary 3, 2024
Get in touch
Have a question an article didn't answer? Talk to a partner.
Get straightforward answers from experienced auditors.