Home / Leadership / Maggie Cheney
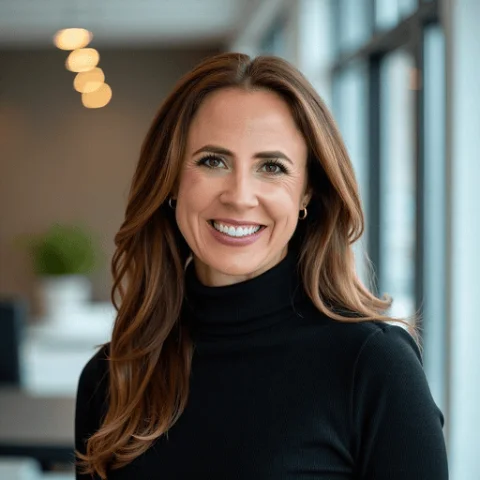
Maggie Cheney
CRISC, ISO 27001 Lead Auditor
Partner
Focus: Risk & IT compliance
- SOC 1
- SOC 2
- HIPAA
- ISO 27001
About Maggie
Maggie has 20 years of experience in Risk Management and IT Compliance. She spent nearly 10 years in KPMG’s IT Advisory and Attestation practice before joining a financial technology company as the Risk and Compliance Director, where she was responsible for implementing the company's Risk and Compliance framework.
She has overseen numerous SOC 1 / SOC 2 audits and other IT compliance audits (HIPAA, ISO) and has vast experience implementing risk management and IT compliance solutions. She is Certified in Risk and Information Systems Control (CRISC) and obtained a Bachelor of Science in Business Administration, Finance, from the University of Colorado at Boulder.
Areas of focus
Core services
Credentials
Professional background
Credentials
- Certified in Risk and Information Systems Control (CRISC)
- ISO/IEC 27001 Lead Auditor (PECB)
- AICPA Advanced SOC for Service Organizations Certificate
Education
- B.S., Business Administration, FinanceUniversity of Colorado Boulder, Leeds School of Business
Articles by Maggie
Insights from Maggie
Management Responsibilities in a SOC Audit: Who Does What?
Not sure what tasks and activities management owns in a SOC audit? An auditor explains management’s responsibilities by phase and where clients often get stuck.
SOC 1What Is SAS 70 Called Now? SOC 1, SSAE 16 & SSAE 18 Explained
SAS 70 is no longer used, but many vendors still reference it. Learn what replaced SAS 70, how SOC 1 reports work, and what to review in a vendor report.
ComplianceUnderstanding Audit Risk & the Audit Risk Model (ARM)
Learn about audit risk, the audit risk model (ARM), and how to reduce risk in SOC 1/SOC 2 audits. An auditor's guide to acceptable risk levels & planning.
Other partners
More of our partners
 Mark LarsonCISSP, CISA, QSA, CMMC Lead Certified Assessor (Lead CCA), CCP, ISO 27001 Lead AuditorPartner
 Lois ColbyCPA, CIA, CISA, CCSK, CMMC Lead Certified Assessor (Lead CCA), ISO 42001 Lead Auditor, ISO 27001 Lead AuditorPartner
 Rhonda WillertCPA, CISSP, CISA, PMP, QSA, ISO 27001 Lead AuditorPartner
 Kevin AndersonCPA, ISO 27001 Lead AuditorPartner
Talk to a partner
Ready to talk?
Connect with Maggie to discuss your IT audit, compliance, or certification needs.