Home / Leadership / Ray Dunham
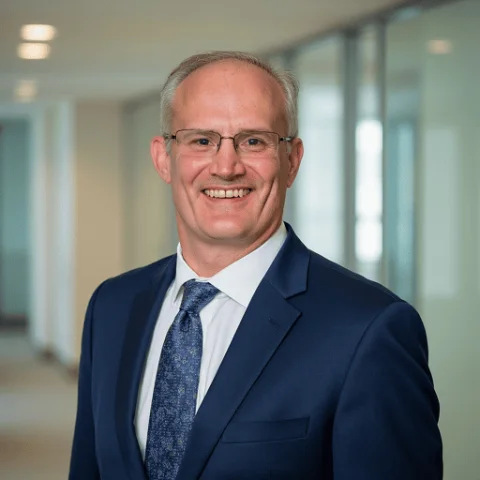
Ray Dunham
CISSP, CISA, GSEC, GWAPT
Partner
Focus: FedRAMP & SOC
- SOC 1
- SOC 2
- FedRAMP
- GovRAMP
About Ray
Ray Dunham started his career as an Air Force Officer in 1996 in the field of Communications and Computer Systems. Following his time in the Air Force, Ray worked in the defense industry in areas of system architecture, system engineering, and primarily information security.
Ray performs FedRAMP assessments and also supports SOC examinations. He brings a practitioner’s understanding of information security to every assessment and works closely with clients to keep each engagement well organized and efficient.
Areas of focus
Core services
Credentials
Professional background
Credentials
- Certified Information Systems Security Professional (CISSP)
- Certified Information Systems Auditor (CISA)
- GIAC Security Essentials (GSEC)
- GIAC Web Application Penetration Tester (GWAPT)
Education
- M.S., TelecommunicationsSouthern Methodist University
- B.S., BiologyUnited States Air Force Academy
Articles by Ray
Insights from Ray
FISMA Compliance: What Federal Agencies & Contractors Must Know
Are you FISMA compliant? Learn what federal agencies and contractors must do, from RMF steps to security controls, to earn and maintain an ATO.
FedRAMPWhat is GovRAMP? A Professional Guide for Compliance
Learn how GovRAMP authorization helps CSPs secure cloud services for state & local governments, including compliance steps, requirements & authorization paths.
FedRAMPFedRAMP 2025 Overhaul: Key Updates to Federal Cloud Security
Explore the FedRAMP 2025 overhaul through the new FedRAMP 20x initiative. Learn how four working groups are modernizing federal cloud security compliance.
Other partners
More of our partners
Talk to a partner
Ready to talk?
Connect with Ray to discuss your IT audit, compliance, or certification needs.