Articles, page 2 of 28
-
FedRAMP
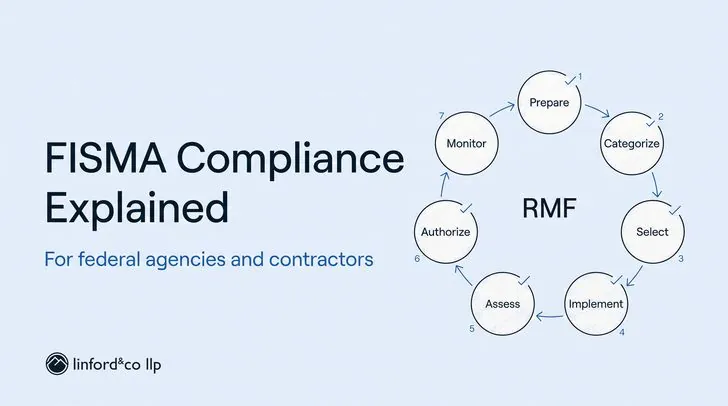
FISMA Compliance Explained: What Federal Agencies & Contractors Need to Know
The Federal Information Security Management Act (FISMA) established the importance of information security principles and practices within the Federal Government.
By Ray DunhamAugust 26, 2026 -
HITRUST
HITRUST 2026 Trust Report: From Supply Chain Attacks to LLM Risks, What CSF v11.8.0 Means for Compliance
HITRUST publishes an annual Trust Report. 2026, however, has been a complex and revealing year for cybersecurity.
By Brian SandenawAugust 19, 2026 -
AI & Emerging Risk
CSA STAR for AI & ISO/IEC 42001: Which Should You Choose?
Companies that use AI as part of their daily practices, and customers of providers that use AI in their business model, are asking which assurance fits best.
By Lois ColbyAugust 12, 2026 -
AI & Emerging Risk
AI Regulatory Compliance in 2026: We Have Seen This Movie Before
No federal law regulates your use of artificial intelligence technology; a few states have binding requirements, and some apply even to organizations convinced they are exempt.
By Richard RiebenAugust 5, 2026 -
Compliance
What Is An Audit? An Auditor's Guide to What Actually Happens
Audits don't have to be intimidating. Learn what an audit is, the most common types, and what the process actually looks like from auditors who do this every day.
By Isaac ClarkeJuly 29, 2026 -
HIPAA
What is HIPAA Compliance? What Auditors Know That the Checklists Don't Tell You
There's no such thing as HIPAA certification, and that's just the start. Learn what HIPAA compliance actually requires, what OCR enforces, and what's changing.
By Rob PierceJuly 22, 2026 -
Compliance
Security Awareness Training Requirements: Who Needs It & What's at Risk
Not sure who needs security awareness training or what auditors expect? Learn who's included, the real risks of gaps, and how AI is changing the rules.
By Hilary StavrakasJuly 15, 2026 -
HIPAA
HIPAA Security Rule Requirements: What’s in Effect, What’s Changing, & What Are Auditors Seeing?
The HIPAA Security Rule faces its biggest proposed update in 20+ years. See what's required now, what's changing, and what auditors are already flagging.
By Danielle PeiJuly 8, 2026 -
Compliance
Don't be Caught Unawares: How to Preserve Audit Evidence when Decommissioning a System!
Decommissioning a system mid-audit cycle? Learn exactly what audit evidence to capture before it goes dark, from access controls to vendor reports and beyond.
By Helen ZellJune 24, 2026 -
Compliance
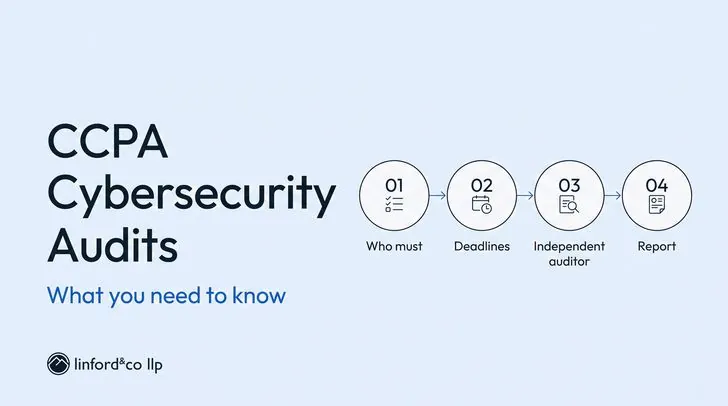
CCPA Cybersecurity Audit Requirements: What You Need to Know
CCPA cybersecurity audit rules took effect in 2026. Learn who's covered, what an independent auditor examines, and whether your program is in compliance.
By Kevin AndersonJune 17, 2026 -
HIPAA
The HIPAA Contingency Plan with a SOC 2 Spin
HIPAA contingency plan rules are changing in 2026. Learn what the five required components are, what auditors commonly find missing, and how to close the gaps.
By Umar AzizJune 10, 2026 -
SOC 2
SOC 2 Physical Security in a Remote-First World: What Auditors Actually Look For
Physical security doesn't disappear in a remote SOC 2: it shifts. Learn what moves to your cloud provider and what auditors still expect from you.
By Jessica KielJune 3, 2026
Get in touch
Have a question an article didn't answer? Talk to a partner.
Get straightforward answers from experienced auditors.