Articles, page 10 of 28
-
CMMC & NIST
Understanding the New NIST Password Guidelines for 2024
Explore the latest NIST password guidelines and their impact. Learn how to implement recommendations while maintaining security and improving user experience.
By Britney OswaldOctober 30, 2024 -
Compliance
What Are Intrusion Detection & Prevention Systems (IDPS) & How Do They Work?
Learn how IDPS (Intrusion Detection & Prevention Systems) work to protect your network. Discover the differences between IDS vss IPS components & their benefits.
By Hilary StavrakasOctober 23, 2024 -
Compliance
Software Supply Chain Security & the Secure Software Development Attestation Form
Introducing the Secure Software Development Attestation Form. Learn about SSDF Attestation, its purpose for software security, & how Linford & Co. can guide you.
By Richard RiebenOctober 16, 2024 -
Compliance
Role-Based Access Control (RBAC): A Key to Streamlined Access Management
Discover how RBAC enhances security and streamlines access management. Learn key components, best practices, and industry examples for effective implementation.
By Danielle PeiOctober 9, 2024 -
FedRAMP
FedRAMP Authorizations: New Paths & Looking to the Future
Explore new FedRAMP authorization options introduced by OMB M-24-15. Learn how these changes impact cloud service providers seeking federal government approval.
By Ray DunhamOctober 2, 2024 -
Compliance
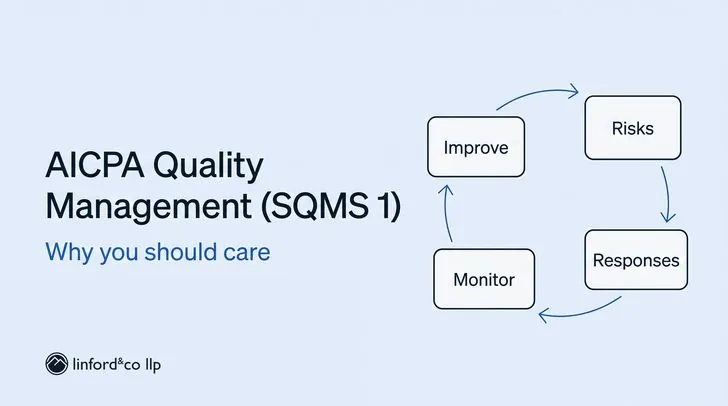
AICPA Quality Management Standard (SQMS) No. 1 (and Why You Should Care)
Learn about the new AICPA Quality Management Standard (SQMS) No. 1, its importance for CPA firms, plus how it impacts attestation services like SOC 1 & SOC 2 reports.
By Lois ColbySeptember 25, 2024 -
PCI DSS
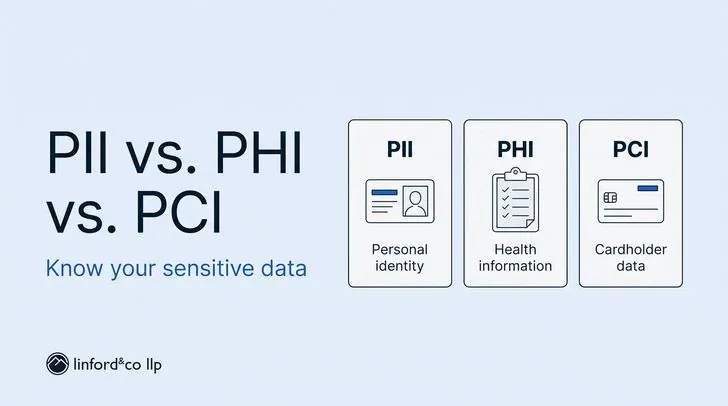
PII, PHI, PCI: Understanding the Differences for Compliance
Understand the key differences between PII, PHI, and PCI data. Learn how to protect sensitive information and ensure compliance with the latest regulations.
By Fred MaldonadoSeptember 18, 2024 -
Compliance
The Cloud Security Alliance (CSA) and the AICPA
What is the relationship between the CSA & the AICPA? Learn how CSA STAR standards overlap with SOC 2 reports to provide data protection in cloud computing environments.
By Megan KovashSeptember 11, 2024 -
Compliance
The Termination Process: Why Interdepartmental Collaboration is the Key to Success!
Interdepartmental collaboration is key for effective termination processes. We cover some common roadblocks and how to establish controls to enhance security.
By Helen ZellAugust 28, 2024 -
AI & Emerging Risk
ISO/IEC 42001:2023 & Its Influence on IT Security Assessments
Introducing ISO/IEC 42001:2023, the new AI governance standard. Learn how ISO 42001 enhances IT security audits, manages AI risk, and ensures ethical AI practices
By Ben BurkettAugust 21, 2024 -
Compliance
Disaster Recovery (DR) Testing: Getting the Most From Your Tabletop Exercise
Learn how to improve DR testing with enhanced tabletop exercises. Discover tips for realistic scenarios, thorough testing, and addressing business-wide impacts.
By Brian SandenawAugust 14, 2024 -
Compliance
What Is The Sarbanes-Oxley Act?
The Sarbanes-Oxley (SOX) Act mandates greater management responsibility and enhanced disclosure of fraud risk for public companies. Read for more details.
By Nicole HemmerAugust 13, 2024
Get in touch
Have a question an article didn't answer? Talk to a partner.
Get straightforward answers from experienced auditors.