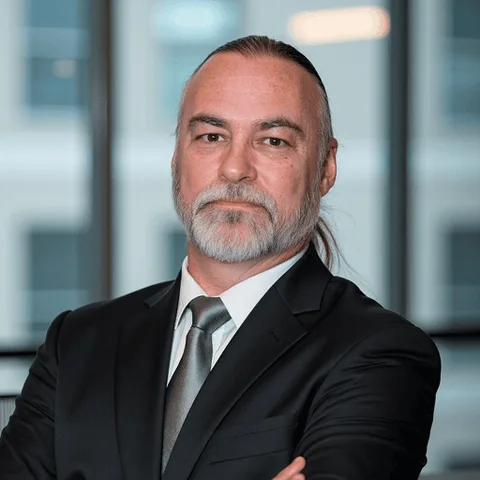
Brian Sandenaw
CISSP, CCSFP, CCSK, CHQP, ISO 27001 Lead Auditor
Director
Focus: HITRUST · ISO 27001 · HIPAA · FedRAMP · PCI DSS
- HIPAA
- HITRUST
- FedRAMP
- ISO 27001
- PCI DSS
About Brian
Brian has over three decades of experience in system administration and information security, having worked at all levels of government (city, county, state, and federal) and with companies ranging from startups to the Fortune 20. He transitioned to auditing in 2018 and has delivered audits and attestations as varied as SOC 1 and SOC 2, HITRUST, FISMA, FERPA, PCI, CSA STAR, and HIPAA.
At Linford & Company, he focuses primarily on HITRUST and SOC 2.
“With a strong background in system administration, information security, and information security leadership, I bring significant real-world experience to the auditing process. I focus primarily on HITRUST, ISO 27001, and CSA STAR assessments.”
Brian Sandenaw
Areas of focus
Core services
Credentials
Professional background
- Certified Information Systems Security Professional (CISSP)
- Certified CSF Practitioner, HITRUST (CCSFP)
- Certificate of Cloud Security Knowledge v5 (CCSK)
- Certified HITRUST Quality Professional (CHQP)
- ISO/IEC 27001 Lead Auditor
Articles by Brian
Insights from Brian
HITRUST 2026 Trust Report & CSF v11.8.0: Key Takeaways
The HITRUST 2026 Trust Report signals a trust crisis, and CSF v11.8.0 is part of the response. Here's what the findings mean and what assessors are seeing.
HITRUSTTrust vs. Verified Trust: The Case for HITRUST
Is your SOC 2 report enough? Learn how HITRUST's Validated Trust model goes beyond attestation to deliver independently verified security assurance.
HITRUSTHITRUST ROI: Is HITRUST Worth It? An External Assessor's View
A Linford & Co external assessor analyzes HITRUST's ROI whitepaper. Learn the real value of HITRUST certification, benefits, and whether it's worth the investment.
Our partners
Meet our partners
Talk to a partner
Ready to talk?
Connect with Brian to discuss your IT audit, compliance, or certification needs.