Home / Leadership / Mark Larson
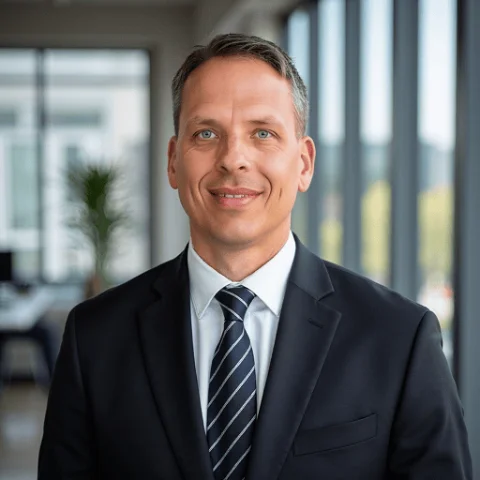
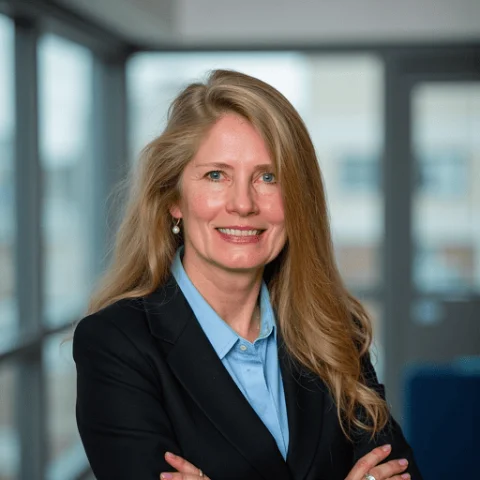
Mark Larson
CISSP, CISA, QSA, CMMC Lead Certified Assessor (Lead CCA), CCP, ISO 27001 Lead Auditor
Partner
Focus: SOC examinations
- SOC 1
- SOC 2
- CMMC
- ISO 27001
- PCI DSS
About Mark
Mark Larson started working in the technology industry in 1998 where he worked in a number of different roles prior to transitioning to the public accounting world in 2004 with Ernst & Young (EY). During his 6 years at EY, Mark provided both assurance and advisory services that spanned multiple industries for both public and private companies.
After leaving EY, Mark filled leadership roles within Internal Audit, Technology, and Security functions for several companies. Mark specializes in SOC examinations and enjoys helping clients establish, formalize, and report on effective control environments while strengthening their security risk profile.
Areas of focus
Core services
Credentials
Professional background
Credentials
- Certified Information Systems Security Professional (CISSP)
- Certified Information Systems Auditor (CISA)
- PCI Qualified Security Assessor (QSA)
- CMMC Lead Certified Assessor (Lead CCA)
- Certified CMMC Professional (CCP)
- ISO/IEC 27001 Lead Auditor (PECB)
- AICPA Advanced SOC for Service Organizations Certificate
- CMMC Advanced Studies Certificate, Saint Louis University
Education
- MBA, AccountingUniversity of Utah, David Eccles School of Business
- B.S., Computer ScienceWeber State University
Articles by Mark
Insights from Mark
GSA Nonfederal CUI Assessments: What Contractors Must Know
GSA ended self-attestation for civilian contractors handling CUI in January 2026. Learn what the assessment requires and where CMMC compliance falls short.
CMMC & NISTCMMC Compliance: A Practical Guide for Defense Contractors
Navigating CMMC compliance? Learn what's required at each level, what assessors actually check, and how to avoid the gaps that derail certifications.
CMMC & NISTNIST SP 800-61 Rev 3: New Incident Response Framework Guide
NIST SP 800-61 Revision 3 replaces the 4-phase lifecycle with CSF 2.0 functions. Learn how to update your incident response plan for CMMC compliance.
Other partners
More of our partners
 Lois ColbyCPA, CIA, CISA, CCSK, CMMC Lead Certified Assessor (Lead CCA), ISO 42001 Lead Auditor, ISO 27001 Lead AuditorPartner
 Rhonda WillertCPA, CISSP, CISA, PMP, QSA, ISO 27001 Lead AuditorPartner
 Kevin AndersonCPA, ISO 27001 Lead AuditorPartner
 Becky McCartyCPA, CISA, CRISC, CIA, CFE, ISO 27001 Lead AuditorPartner
Talk to a partner
Ready to talk?
Connect with Mark to discuss your IT audit, compliance, or certification needs.