Home / Blog / Ray Dunham / Page 2
Insights
Articles by Ray Dunham
23 articles by Ray Dunham, partner. View Ray’s profile.
Articles, page 2 of 2
-
Compliance
Logging and Monitoring - An Essential Part of Every Security Program
Logging and monitoring has a special organizational role to support and provide insight into all the other key areas of a security program. Learn more.
By Ray DunhamSeptember 18, 2019 -
FedRAMP
FedRAMP 3PAOs: What is Their Role in the FedRAMP Process?
A FedRAMP 3PAO is an independent firm that specializes in performing security assessments of commercial CSPs and save them time and money. Learn how!
By Ray DunhamApril 17, 2019 -
FedRAMP
What is FedRAMP? 5 Considerations Before Taking the Leap
FedRAMP is a government program designed to bring consistent and repeatable processes to security evaluations of cloud service offerings (CSO) for the federal government.
By Ray DunhamFebruary 27, 2019 -
FedRAMP
FedRAMP vs. FISMA: What You Need To Know
Both FedRAMP and FISMA aim to reduce information security risk within federal information systems. Learn their key differences and similarities.
By Ray DunhamJanuary 9, 2019 -
Compliance
What is Cryptojacking and How to Protect Yourself
Although cryptojacking is less damaging than most cyber attacks, it’s still serious. The delivery mechanisms and code will continue to evolve. Stay informed!
By Ray DunhamAugust 1, 2018 -
Compliance
GDPR Compliance Checklist: Key Tasks for Organizations to Complete
If your organization transmits, receives, processes, or stores data relating to EU citizens, you are impacted by the GDPR. Our compliance checklist will help.
By Ray DunhamJune 6, 2018 -
Compliance
Security Procedures - How Do They Fit Into My Overall Security Documentation Library?
Go beyond security policies and understand the importance of security procedures, how they fit into your overall security documentation library, and find principles to keep in mind of when drafting your security procedures.
By Ray DunhamMarch 14, 2018 -
FedRAMP
The FedRAMP SSP: Important Tips for a Successful Outcome
The FedRAMP System Security Plan (SSP) is the foundational document that supports a FedRAMP assessment. A poorly written SSP or one that excludes important control implementations will only delay the assessment process and cost the CSP valuable time and resources. Learn how to make yours a success!
By Ray DunhamJanuary 31, 2018 -
FedRAMP
FedRAMP Continuous Monitoring - What Are the Responsibilities of CSPs and 3PAOs?
Learn the specific FedRAMP continuous monitoring requirements and some things to keep in mind when preparing to address these requirements.
By Ray DunhamSeptember 27, 2017 -
Compliance
How Is Your (Cyber) Hygiene?
When most people think of hygiene, I would venture to say that technology or computer systems are not part of the mental picture. There are interesting parallels, however, between what we think of as “normal” hygiene and cyber hygiene.
By Ray DunhamFebruary 21, 2017 -
Compliance
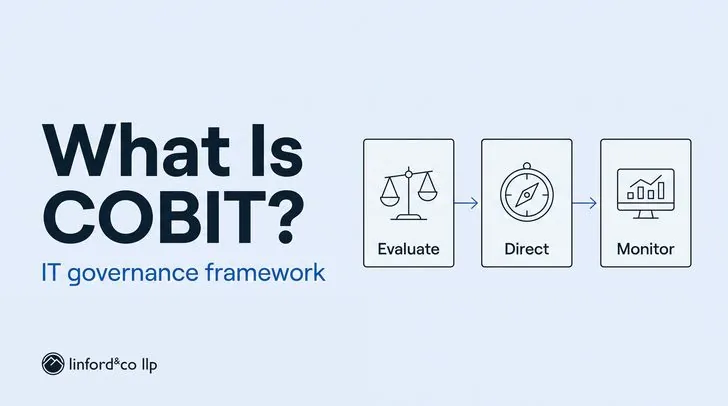
What Is COBIT®?
COBIT® stands for Control Objectives for Information and Related Technology. What is it? Put simply, it is a framework for enterprise wide governance to include business functions, information and information technology resources. The COBIT® framework provides a structure upon which to build an enterprise governance program.
By Ray DunhamSeptember 6, 2016
Get in touch
Have a question an article didn't answer? Talk to a partner.
Get straightforward answers from experienced auditors.